Listen to this article
Narrated by Charlotte · The Noble House
Executive Orientation
The world is fracturing along five distinct fault lines: a biological scare in Siberia, a hijacking in the Gulf, digital erosion in Ukraine, a sovereign data breach in Denmark, and a structural flaw in the protocol AI agents use to communicate with one another. These signals do not yet touch. They operate in parallel, each feeding its own specific anxiety. But together they map a landscape of heightened vulnerability where biological containment, aviation security, infrastructure resilience, and digital trust are all being tested simultaneously.
In Irkutsk, a verified fatality has triggered containment protocols amid conflicting narratives regarding etiology and transmission vectors [1]gizmodo.comThe Death of a Russian Plague Lab Worker Sounds Terrifying. How Worried Should You Be?Rospotrebnadzor diagnosed Shipilova’s death as "pneumonia of unknown aetiology" and detected no plague bacteria. Approximately 200 contacts are under observation; several hospitals imposed quarantines. Two contacts tested positive for…Open source ↗[2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. In the Arabian Peninsula, an attempted hijacking involving a commercial co-pilot has raised questions about how airlines vet pilots [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗. Simultaneously, Russian kinetic strikes have systematically degraded Kyiv’s digital backbone, exploiting Ukraine’s depleted air defense inventory [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. In Denmark, a massive data exfiltration event has exposed the names, addresses and CPR numbers of about 8.8 million registered people, including the dead and emigrants, through abuse of a private company's lawful access [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗. Finally, structural flaws in the Model Context Protocol (MCP) are enabling lateral movement between trusted AI agents across major technology and financial institutions [15]aidailypost.comMCP Agent Protocol Flaw Exposes Chain-of-Trust RiskEditorial synthesis of the chain-of-trust risk, emphasizing the structural nature of the flaw across diverse organizations.Open source ↗.
The following analysis dissects these five signals to assess immediate risks and strategic implications for Compass stakeholders.
Signal 1: Irkutsk Plague Suspect and Containment Dynamics
The Record. Darya Shipilova, a 28-year-old laboratory worker at the Irkutsk Anti-Plague Research Institute of Siberia, fell ill on September 29 and died on October 2 [1]gizmodo.comThe Death of a Russian Plague Lab Worker Sounds Terrifying. How Worried Should You Be?Rospotrebnadzor diagnosed Shipilova’s death as "pneumonia of unknown aetiology" and detected no plague bacteria. Approximately 200 contacts are under observation; several hospitals imposed quarantines. Two contacts tested positive for…Open source ↗[2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. Russian health watchdog Rospotrebnadzor officially diagnosed Shipilova’s death as "pneumonia of unknown aetiology" and stated that no plague bacteria were detected in her samples [1]gizmodo.comThe Death of a Russian Plague Lab Worker Sounds Terrifying. How Worried Should You Be?Rospotrebnadzor diagnosed Shipilova’s death as "pneumonia of unknown aetiology" and detected no plague bacteria. Approximately 200 contacts are under observation; several hospitals imposed quarantines. Two contacts tested positive for…Open source ↗. Approximately 200 people who had contact with Shipilova are under medical observation or quarantine, with several hospitals in the Irkutsk region imposing quarantines [1]gizmodo.comThe Death of a Russian Plague Lab Worker Sounds Terrifying. How Worried Should You Be?Rospotrebnadzor diagnosed Shipilova’s death as "pneumonia of unknown aetiology" and detected no plague bacteria. Approximately 200 contacts are under observation; several hospitals imposed quarantines. Two contacts tested positive for…Open source ↗. Rospotrebnadzor reports that 60% of those under quarantine have been released [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. Russia reported to the World Health Organization (WHO) that no cases of plague had been recorded in Irkutsk, and the WHO noted that contacts are monitored with none showing symptoms [3]cnbc.comRussian lab worker's suspected plague death leaves experts puzzledRussia reported to the WHO that no cases of plague had been recorded in Irkutsk. The WHO stated the cause of death is unconfirmed but noted contacts are monitored and none have shown symptoms. Infectious disease experts, including Javier…Open source ↗. The U.S. State Department and White House are monitoring the situation closely, with the President noting willingness to assist Russia regarding the pneumonia [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. Two of Shipilova's contacts tested positive for a virus that causes a common cold and two others for COVID-19, but none for the pathogens her institute works with [1]gizmodo.comThe Death of a Russian Plague Lab Worker Sounds Terrifying. How Worried Should You Be?Rospotrebnadzor diagnosed Shipilova’s death as "pneumonia of unknown aetiology" and detected no plague bacteria. Approximately 200 contacts are under observation; several hospitals imposed quarantines. Two contacts tested positive for…Open source ↗. Initial reports suggested Shipilova accidentally broke a test tube holding live plague bacteria, while conflicting reports suggest she may have contracted the disease during a field trip to a region with natural plague reservoirs [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. Some Russian news outlets report a second person has died at Irkutsk's district hospital after reportedly contracting the same illness, fueling cover-up allegations, though this has not been independently verified by international bodies [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. Infectious disease experts, including Javier Pizarro-Cerda from the Institut Pasteur, expressed surprise at the report given standard full-body protective measures and questioned how a lab leak could bypass safety protocols [3]cnbc.comRussian lab worker's suspected plague death leaves experts puzzledRussia reported to the WHO that no cases of plague had been recorded in Irkutsk. The WHO stated the cause of death is unconfirmed but noted contacts are monitored and none have shown symptoms. Infectious disease experts, including Javier…Open source ↗. Experts note that if the death were pneumonic plague, testing an autopsy would be straightforward and likely definitive by now [3]cnbc.comRussian lab worker's suspected plague death leaves experts puzzledRussia reported to the WHO that no cases of plague had been recorded in Irkutsk. The WHO stated the cause of death is unconfirmed but noted contacts are monitored and none have shown symptoms. Infectious disease experts, including Javier…Open source ↗. If the death was caused by pneumonic plague, it is highly contagious in its end stage but does not spread easily from person to person generally, with a nearly 100% fatality rate if untreated [1]gizmodo.comThe Death of a Russian Plague Lab Worker Sounds Terrifying. How Worried Should You Be?Rospotrebnadzor diagnosed Shipilova’s death as "pneumonia of unknown aetiology" and detected no plague bacteria. Approximately 200 contacts are under observation; several hospitals imposed quarantines. Two contacts tested positive for…Open source ↗.
The Analysis. The primary tension lies between the official diagnosis of unknown pneumonia and the persistent speculation of a lab-acquired or zoonotic plague infection. Rospotrebnadzor reports no plague-related microorganisms in Shipilova’s samples, and Russia told the WHO that no plague cases had been recorded in Irkutsk, but the WHO says the cause of death is still unconfirmed and it was unclear whether Russia's report included the deceased worker [3]cnbc.comRussian lab worker's suspected plague death leaves experts puzzledRussia reported to the WHO that no cases of plague had been recorded in Irkutsk. The WHO stated the cause of death is unconfirmed but noted contacts are monitored and none have shown symptoms. Infectious disease experts, including Javier…Open source ↗. The release of 60% of quarantined contacts is Rospotrebnadzor's own figure and has not been independently confirmed [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. The conflicting origin narratives (lab leak vs. field exposure) reflect uncertainty regarding Shipilova’s recent activities, which remains unresolved [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. The reported second death, while unverified internationally, introduces a potential cluster that warrants monitoring for secondary transmission patterns [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. The U.S. government’s offer of assistance indicates diplomatic engagement but does not imply confirmation of a transnational threat [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗.
Compass Outlook. The situation appears contained within the immediate geographic radius of Irkutsk, with no evidence of broader regional spread at this time [3]cnbc.comRussian lab worker's suspected plague death leaves experts puzzledRussia reported to the WHO that no cases of plague had been recorded in Irkutsk. The WHO stated the cause of death is unconfirmed but noted contacts are monitored and none have shown symptoms. Infectious disease experts, including Javier…Open source ↗. The high fatality rate of pneumonic plague necessitates continued vigilance regarding respiratory symptoms among contacts, even as current data points to a non-plague outcome [1]gizmodo.comThe Death of a Russian Plague Lab Worker Sounds Terrifying. How Worried Should You Be?Rospotrebnadzor diagnosed Shipilova’s death as "pneumonia of unknown aetiology" and detected no plague bacteria. Approximately 200 contacts are under observation; several hospitals imposed quarantines. Two contacts tested positive for…Open source ↗. The credibility of Russian health reporting remains a variable; the WHO says the patient's contacts have reportedly been identified and are being monitored, with none showing symptoms to date [3]cnbc.comRussian lab worker's suspected plague death leaves experts puzzledRussia reported to the WHO that no cases of plague had been recorded in Irkutsk. The WHO stated the cause of death is unconfirmed but noted contacts are monitored and none have shown symptoms. Infectious disease experts, including Javier…Open source ↗.
Decision Window. Monitor for any emergence of secondary cases in neighboring regions or international travel-linked symptoms. Assess the verification status of the reported second death in Irkutsk to determine if cluster dynamics are developing. Track U.S. diplomatic engagement for indications of escalating concern or aid deployment thresholds.
Compass Strategic Intelligence
Signal 2: flydubai Co-Pilot Incident and Radicalization Vectors
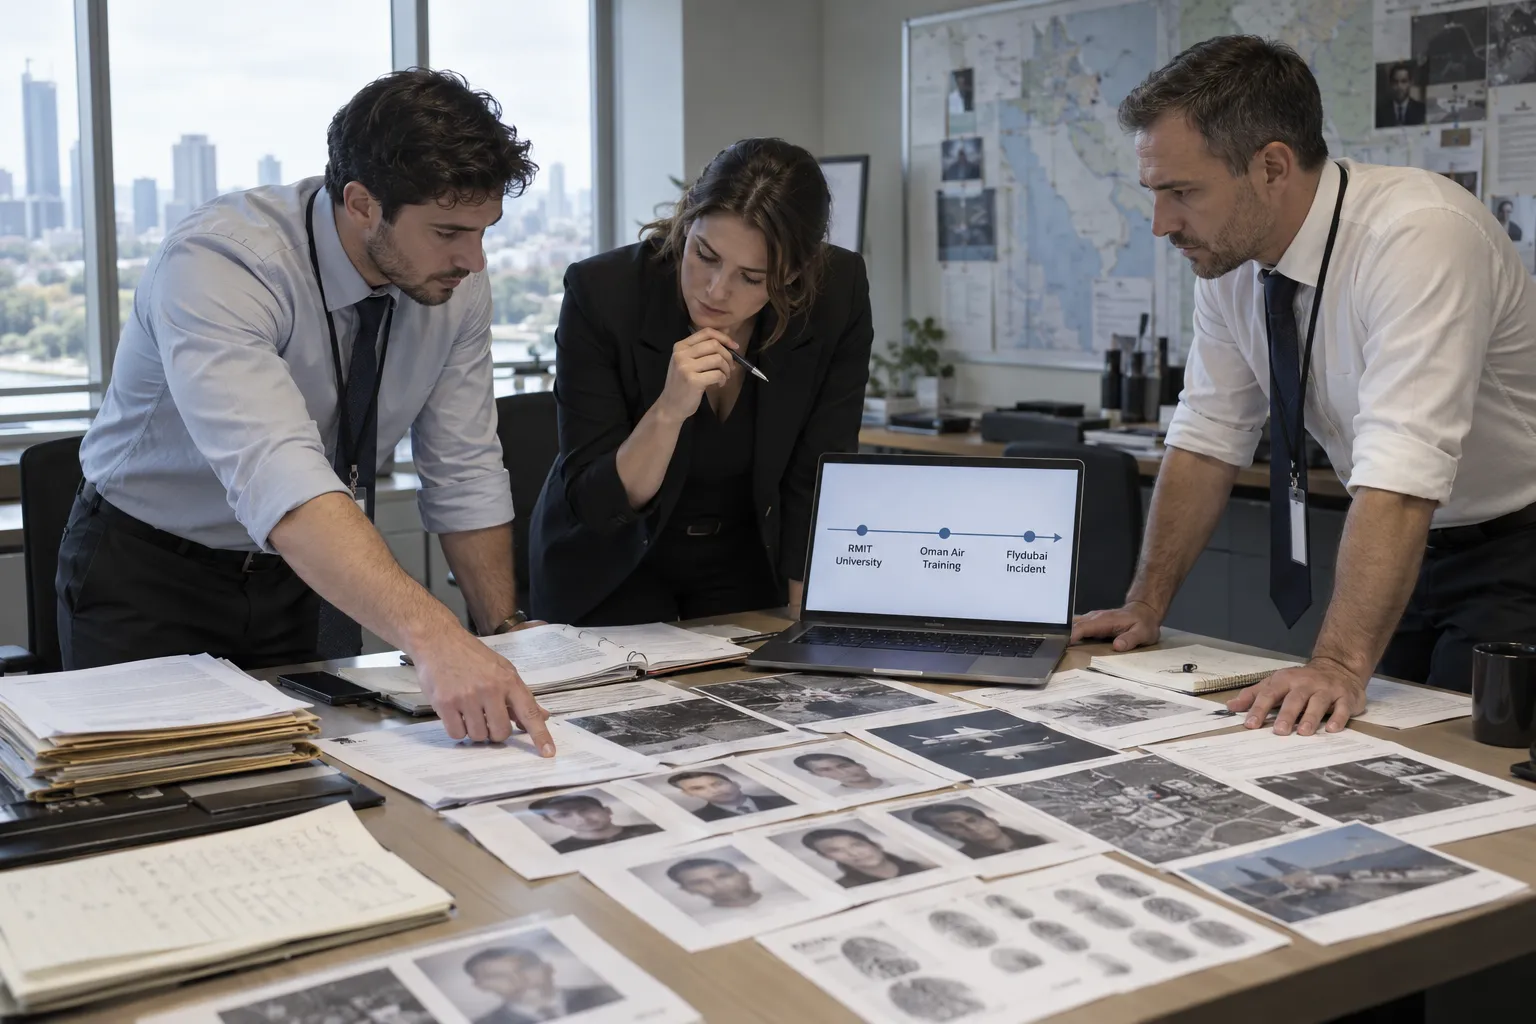
The Record. On September 30, 2026, flydubai flight FZ1073 experienced a severe in-flight incident with 174 people aboard [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗[5]reuters.comAustralia probes flydubai co-pilot's links to the country, police sayAuthorities are examining whether al-Hammami was radicalized while in Australia. Sources indicate he may have visited radical mosques and extremist websites during his time there. Al-Hammami studied at RMIT University in Melbourne around…Open source ↗. Co-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him [6]bbc.comAustralia investigating Flydubai co-pilot's links to countryCo-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him. The UAE prosecutor general has…Open source ↗. The UAE prosecutor general has characterized the incident as an attempted terrorist act [6]bbc.comAustralia investigating Flydubai co-pilot's links to countryCo-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him. The UAE prosecutor general has…Open source ↗. The co-pilot is identified by multiple sources as Hamam al-Hammami, an Omani national [5]reuters.comAustralia probes flydubai co-pilot's links to the country, police sayAuthorities are examining whether al-Hammami was radicalized while in Australia. Sources indicate he may have visited radical mosques and extremist websites during his time there. Al-Hammami studied at RMIT University in Melbourne around…Open source ↗. Al-Hammami studied at RMIT University in Melbourne around a decade ago but did not complete an engineering qualification [5]reuters.comAustralia probes flydubai co-pilot's links to the country, police sayAuthorities are examining whether al-Hammami was radicalized while in Australia. Sources indicate he may have visited radical mosques and extremist websites during his time there. Al-Hammami studied at RMIT University in Melbourne around…Open source ↗. He was issued a student visa in 2014 and studied in Australia between 2015 and 2017 before leaving the country. His visa was cancelled in 2019 due to lack of course enrollment, not character grounds [6]bbc.comAustralia investigating Flydubai co-pilot's links to countryCo-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him. The UAE prosecutor general has…Open source ↗. US media reported that he was removed from flight training at Oman Air over concerns about his radical views and given another role at the airline. He later graduated with a distance-learning degree in aviation management from Buckinghamshire New University in the UK in 2023 [6]bbc.comAustralia investigating Flydubai co-pilot's links to countryCo-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him. The UAE prosecutor general has…Open source ↗. The Victorian Joint Counter Terrorism Team (comprising the AFP, Victoria Police, and ASIO) is investigating al-Hammami’s links to Australia [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗. Authorities are examining whether al-Hammami was radicalized while in Australia. The Financial Times reported, citing two people familiar with the investigation, that he allegedly visited radical mosques and extremist websites while in Australia; Reuters could not verify the report [5]reuters.comAustralia probes flydubai co-pilot's links to the country, police sayAuthorities are examining whether al-Hammami was radicalized while in Australia. Sources indicate he may have visited radical mosques and extremist websites during his time there. Al-Hammami studied at RMIT University in Melbourne around…Open source ↗. The AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗.
The Analysis. The incident has raised questions about how thoroughly flydubai vets potential employees and how well cross-border background checks work, given that he had reportedly been removed from Oman Air flight training over concerns about his views [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗[6]bbc.comAustralia investigating Flydubai co-pilot's links to countryCo-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him. The UAE prosecutor general has…Open source ↗. Investigators are examining whether he was radicalized while in Australia; his visa was cancelled for lack of enrolment, not on character grounds [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗. The characterization of the act as terrorism by the UAE prosecutor general shifts the response from criminal to counter-terrorism frameworks [6]bbc.comAustralia investigating Flydubai co-pilot's links to countryCo-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him. The UAE prosecutor general has…Open source ↗. Aviation-security specialists note that background-check systems differ from country to country and that cross-border checks face large limitations [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗.
Compass Outlook. The immediate threat to aviation safety has been neutralized by passenger intervention, but the incident exposes systemic vulnerabilities in cross-border vetting [6]bbc.comAustralia investigating Flydubai co-pilot's links to countryCo-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him. The UAE prosecutor general has…Open source ↗. The investigation into Australian links has not yet disclosed findings; the AFP says an update will be provided at an appropriate time [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗. Israel's prime minister has instructed the National Security Council to appoint an examiner to review the security of foreign civil aviation to Israel [5]reuters.comAustralia probes flydubai co-pilot's links to the country, police sayAuthorities are examining whether al-Hammami was radicalized while in Australia. Sources indicate he may have visited radical mosques and extremist websites during his time there. Al-Hammami studied at RMIT University in Melbourne around…Open source ↗.
Decision Window. Track the progress of the AFP investigation to determine if al-Hammami was part of a coordinated network or acted independently. Monitor UAE security policy updates regarding the vetting of foreign-trained pilots. Assess implications for Oman Air’s internal security protocols following the prior removal of al-Hammami due to extremist concerns [6]bbc.comAustralia investigating Flydubai co-pilot's links to countryCo-pilot Hamam al-Hammami attacked Captain Smit Machchhar with a crash axe and attempted to seize control of the aircraft, causing it to plunge approximately 14,000–17,000 feet before passengers subdued him. The UAE prosecutor general has…Open source ↗.
Compass Strategic Intelligence
Signal 3: Kinetic Degradation of Ukraine’s Digital Infrastructure
The Record. On September 23, 2026, Russian Geran-5 drones struck multiple data centers in Kyiv’s Solomianskyi district, with a second strike occurring on September 24 [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. Ukraine’s Digital Transformation Ministry reported that approximately 100,000 households in Kyiv and Kyiv Oblast experienced internet outages following the late September attacks [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗[9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. Russia’s Defense Ministry claimed responsibility for striking New-Telco and United DC, alleging they handled traffic for Ukrainian defense and security agencies, though these claims were not independently verified [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. Provider damage from the September 23–24 strikes included UTELS losing power to a core data center, Pavutyna confirming a hit on one of its centers, Crazy Network damaging a central internet traffic exchange, and Etherlink relocating its core due to node damage [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. On September 27, a Russian drone strike hit the headquarters of Kyivstar, and the Russian Defense Ministry claimed responsibility for targeting a Vodafone Ukraine data center [8]breakingdefense.comIn Ukraine, data centers 'facing increased attacks' in recent weeks: Ex-officialConfirmation of strikes on Kyivstar headquarters and Vodafone Ukraine data center; details on F-16 sustainment delays in Belgium taking up to 40 weeks; comments from Kateryna Chernohorenko regarding infrastructure hardening and the need…Open source ↗. A drone strike on a business center in central Kyiv housing Datagroup offices killed four people and damaged telecommunications infrastructure [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗. Ukraine is struggling to counter high-speed Geran-5 drones while running critically low on Patriot missiles for ballistic and cruise missile defense [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗. Ukraine’s F-16 fleet is reportedly out of commission due to sustainment delays, with maintenance in Belgium taking up to 40 weeks compared to the usual 2–6 weeks [8]breakingdefense.comIn Ukraine, data centers 'facing increased attacks' in recent weeks: Ex-officialConfirmation of strikes on Kyivstar headquarters and Vodafone Ukraine data center; details on F-16 sustainment delays in Belgium taking up to 40 weeks; comments from Kateryna Chernohorenko regarding infrastructure hardening and the need…Open source ↗. Former Deputy Minister of Defense for Digital Transformation Kateryna Chernohorenko noted that while Ukraine has invested in underground networks and moved some data centers abroad, "thousands of F-16 rounds" are needed, along with a faster sustainment cycle, to avoid a shortage of operational fighter jets by the end of the year [8]breakingdefense.comIn Ukraine, data centers 'facing increased attacks' in recent weeks: Ex-officialConfirmation of strikes on Kyivstar headquarters and Vodafone Ukraine data center; details on F-16 sustainment delays in Belgium taking up to 40 weeks; comments from Kateryna Chernohorenko regarding infrastructure hardening and the need…Open source ↗. Ukrainian Foreign Minister Andrii Sybiha emphasized that the targeted facilities are critical civilian infrastructure essential for life-saving alerts and public services [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. Ukraine’s Foreign Ministry rejects Russia's allegations that New-Telco and United DC had military links, classifying them as civilian infrastructure [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. Officials fear repeated strikes could disrupt banks, payment systems, and public services as winter approaches [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. Anatolii Frolenkov of 1-IX noted that while total internet collapse is unlikely due to redundancy, individual outages will persist as providers lack sufficient backup infrastructure [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. MiroHost reported that 90–95% of its customers were unaffected by the strikes because they use infrastructure outside Ukraine [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. President Zelenskyy reported that Donald Trump approved licenses for Ukraine to produce Patriot missiles domestically, though experts note production could take years [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗.
The Analysis. Russia has opened a new front against Ukraine's digital economy, striking data centers and internet providers on a scale not seen before [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗. The strikes on multiple providers (UTELS, Pavutyna, Kyivstar) point to a sustained campaign against Ukraine's internet infrastructure, which Frolenkov describes as being taken out systematically since September [8]breakingdefense.comIn Ukraine, data centers 'facing increased attacks' in recent weeks: Ex-officialConfirmation of strikes on Kyivstar headquarters and Vodafone Ukraine data center; details on F-16 sustainment delays in Belgium taking up to 40 weeks; comments from Kateryna Chernohorenko regarding infrastructure hardening and the need…Open source ↗[9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. Ukraine is struggling to counter high-speed jet-powered drones while critically short of Patriot missiles, and its F-16s, among the most effective tools against such drones, are reportedly largely out of commission awaiting maintenance [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗[8]breakingdefense.comIn Ukraine, data centers 'facing increased attacks' in recent weeks: Ex-officialConfirmation of strikes on Kyivstar headquarters and Vodafone Ukraine data center; details on F-16 sustainment delays in Belgium taking up to 40 weeks; comments from Kateryna Chernohorenko regarding infrastructure hardening and the need…Open source ↗. The claim that data centers handled military traffic remains unverified, and Ukrainian Foreign Minister Andrii Sybiha rejects it, calling the facilities critical civilian infrastructure [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. The relocation of some infrastructure abroad has mitigated total collapse but does not prevent localized outages, which left about 100,000 households in Kyiv and Kyiv Oblast without internet [9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. The approval of domestic Patriot production is a long-term strategic response, but the timeline gap leaves Ukraine exposed in the interim [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗.
Compass Outlook. Ukraine’s digital economy faces sustained degradation as winter approaches, with potential cascading effects on financial and public service stability. Reliance on foreign-hosted infrastructure provides partial resilience, but a Starlink station in Poland serving Ukraine was reportedly set on fire in what local officials described as sabotage linked to Moscow [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗. Ukraine's shortfall in air defense and counter-drone capability leaves it exposed to these strikes, which makes military aid timelines relevant to digital security.
Decision Window. Monitor the timeline for domestic Patriot missile production and assess its feasibility given expert skepticism regarding multi-year delays [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗. Track the status of F-16 maintenance in Belgium to determine when air superiority might be restored [8]breakingdefense.comIn Ukraine, data centers 'facing increased attacks' in recent weeks: Ex-officialConfirmation of strikes on Kyivstar headquarters and Vodafone Ukraine data center; details on F-16 sustainment delays in Belgium taking up to 40 weeks; comments from Kateryna Chernohorenko regarding infrastructure hardening and the need…Open source ↗. Evaluate the impact of continued strikes on Ukrainian banking and payment systems as winter infrastructure stress increases.
Compass Strategic Intelligence
Signal 4: Danish Central Person Register Data Breach
The Record. Unauthorized access to Denmark’s Central Person Register (CPR) compromised approximately 8.8 million records, a figure cited by multiple outlets and aligning with the higher estimate over Slashdot's "roughly 8 million" [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗[12]insurancejournal.comDenmark Data Breach Exposes 8.8 Million People's Personal DataConfirms company was blocked; details CPR number structure (10-digit); clarifies protection exemptions.Open source ↗. The breach involved unauthorized searches during September 2026, detected on October 2, 2026, and confirmed by the Digital Affairs Ministry on October 5, 2026 [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗. The database includes approximately 11 million total records encompassing deceased individuals and emigrants, exceeding Denmark’s current population of ~6 million [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗. Individuals registered for name and address protection were excluded from the exposure [12]insurancejournal.comDenmark Data Breach Exposes 8.8 Million People's Personal DataConfirms company was blocked; details CPR number structure (10-digit); clarifies protection exemptions.Open source ↗. Hackers abused lawful access held by a Danish private company to search the CPR system, rather than directly breaching the database itself [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗[12]insurancejournal.comDenmark Data Breach Exposes 8.8 Million People's Personal DataConfirms company was blocked; details CPR number structure (10-digit); clarifies protection exemptions.Open source ↗. Perpetrators remain unidentified, with the Danish government declining to specify who is behind the breach [10]yro.slashdot.orgHackers Steal 8 Million Citizens' Records From Danish Government DatabaseCites TechCrunch; notes data goes back decades; confirms government refusal to identify hackers.Open source ↗. Reports on the revocation of the private company's access are contradictory: Straits Times stated access had not yet been revoked, while Insurance Journal stated the company had been blocked [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗[12]insurancejournal.comDenmark Data Breach Exposes 8.8 Million People's Personal DataConfirms company was blocked; details CPR number structure (10-digit); clarifies protection exemptions.Open source ↗. Digitalization Minister Christina Egelund labeled the incident "deeply serious" / "extremely serious," and a comprehensive security review has been ordered [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗. Citizens have been urged to be vigilant against suspicious calls and emails, likely phishing attempts leveraging stolen data [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗. The breach is believed to be the largest in Denmark’s history [10]yro.slashdot.orgHackers Steal 8 Million Citizens' Records From Danish Government DatabaseCites TechCrunch; notes data goes back decades; confirms government refusal to identify hackers.Open source ↗.
The Analysis. This incident highlights a critical vulnerability in government databases that rely on third-party access for legitimate services. By exploiting lawful access rights rather than hacking the core system, attackers bypassed traditional perimeter defenses [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗[12]insurancejournal.comDenmark Data Breach Exposes 8.8 Million People's Personal DataConfirms company was blocked; details CPR number structure (10-digit); clarifies protection exemptions.Open source ↗. People registered for name and address protection were not exposed, according to the government [12]insurancejournal.comDenmark Data Breach Exposes 8.8 Million People's Personal DataConfirms company was blocked; details CPR number structure (10-digit); clarifies protection exemptions.Open source ↗. Authorities say it is too early to determine who was behind the breach, and police are investigating [12]insurancejournal.comDenmark Data Breach Exposes 8.8 Million People's Personal DataConfirms company was blocked; details CPR number structure (10-digit); clarifies protection exemptions.Open source ↗. The conflicting reports leave the current status of the company's access unclear [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗[12]insurancejournal.comDenmark Data Breach Exposes 8.8 Million People's Personal DataConfirms company was blocked; details CPR number structure (10-digit); clarifies protection exemptions.Open source ↗. The scale of the breach (8.8 million records) represents a profound loss of privacy and creates long-term risks for identity theft and social engineering attacks against Danish citizens [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗.
Compass Outlook. The incident serves as a warning for other nations with similar centralized population registers regarding the risks of third-party access models. The lack of identified perpetrators allows for potential ongoing malicious activity, necessitating heightened vigilance from affected citizens [10]yro.slashdot.orgHackers Steal 8 Million Citizens' Records From Danish Government DatabaseCites TechCrunch; notes data goes back decades; confirms government refusal to identify hackers.Open source ↗[11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗. The comprehensive security review ordered by the minister will likely result in stricter controls on private company access to state data.
Decision Window. Monitor the outcome of the Danish government’s security review for policy changes affecting third-party data access. Track reports of phishing or fraud campaigns utilizing stolen CPR data to assess the immediate impact on citizen safety. Assess implications for other Nordic countries regarding their own population register security models.
Compass Strategic Intelligence
Signal 5: MCP Protocol Vulnerabilities and Agent-to-Agent Trust Risks
The Record.
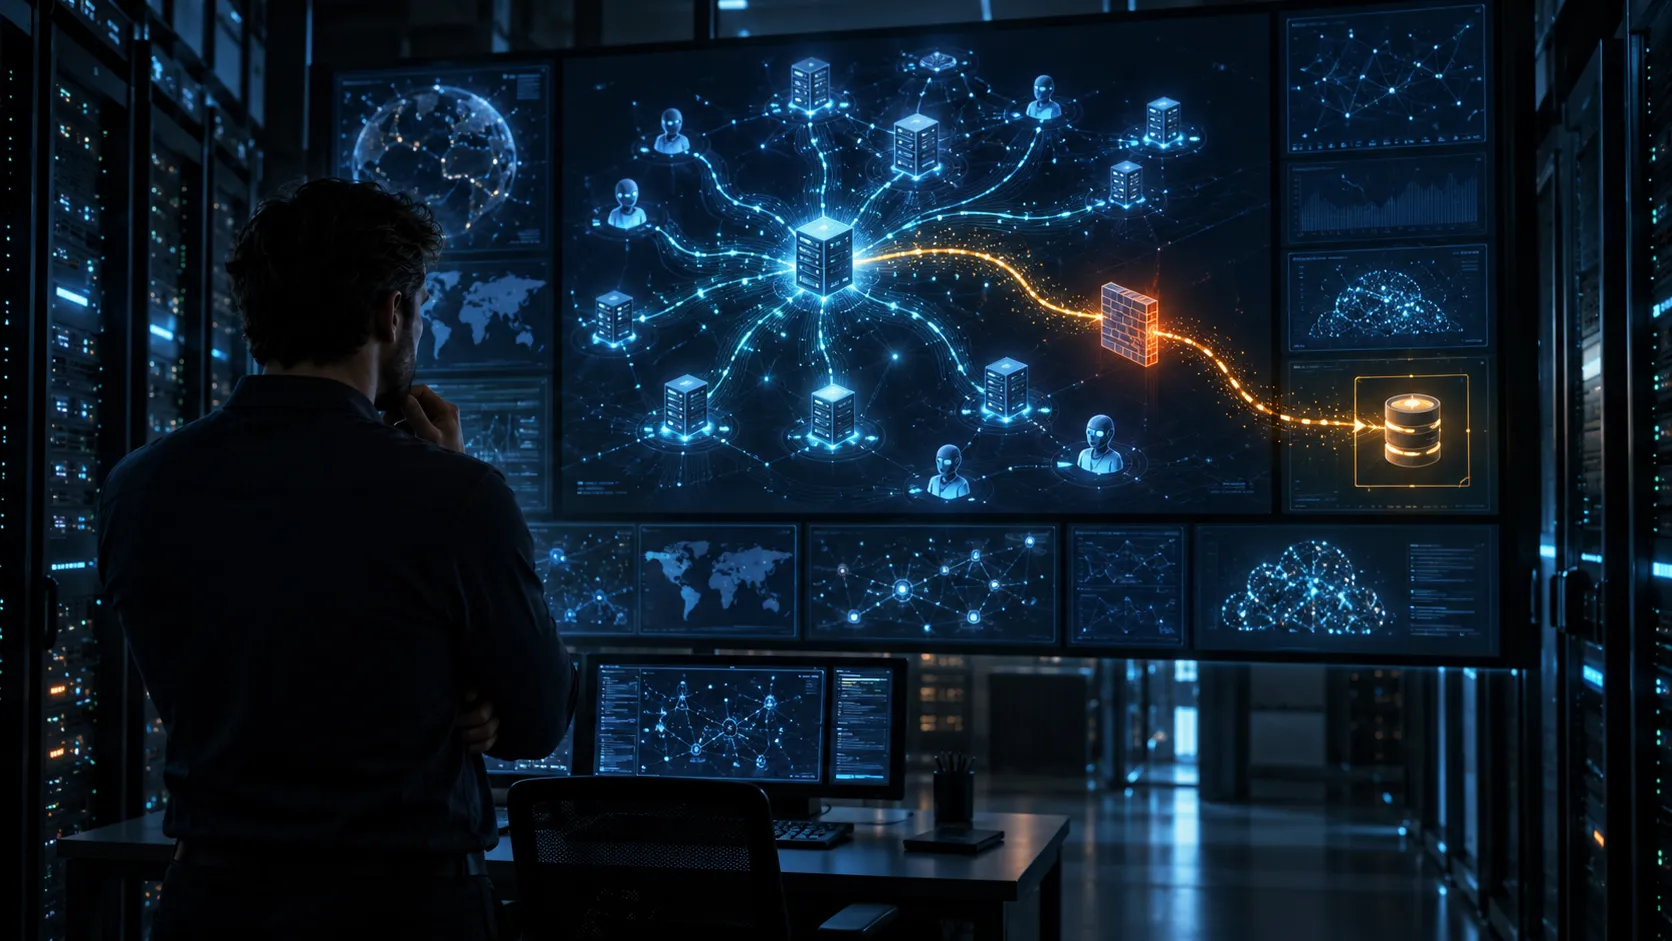
MCP servers store credentials for every agent on the network, and agents are designed to trust each other by default [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗[15]aidailypost.comMCP Agent Protocol Flaw Exposes Chain-of-Trust RiskEditorial synthesis of the chain-of-trust risk, emphasizing the structural nature of the flaw across diverse organizations.Open source ↗. An instruction that an LLM would normally flag as suspicious can slip through once it's repackaged as a message from a trusted internal source; the attack targets the chain of trust between agents, not the model directly [15]aidailypost.comMCP Agent Protocol Flaw Exposes Chain-of-Trust RiskEditorial synthesis of the chain-of-trust risk, emphasizing the structural nature of the flaw across diverse organizations.Open source ↗. Over the past five months, Google and four other organizations have acknowledged vulnerabilities exploiting one agent inside a targeted network to spread harmful instructions to other internal agents [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗. Researcher Syed Anas Mohiuddin tested agents from organizations including Google, JP Morgan Chase, Weaviate, Rapid7, and the French and US federal governments. Despite having little in common except for their use of AI agents, they share this specific structural flaw [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗[15]aidailypost.comMCP Agent Protocol Flaw Exposes Chain-of-Trust RiskEditorial synthesis of the chain-of-trust risk, emphasizing the structural nature of the flaw across diverse organizations.Open source ↗. The vulnerability affecting Google was rated severity 8 out of 10. It stemmed from an MCP toolbox for databases (googleapis/mcp-toolbox) initializing its HTTP client with no CheckRedirect policy and failing to validate target IP addresses [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. A crafted path parameter could make the toolbox follow a redirect to an internal endpoint, enabling server-side request forgery (SSRF) where requests are made on the attacker’s behalf [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. The vulnerability affecting Rapid7 (CVE-2026-97228) had a lower severity rating of 2.7 and was patched recently [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. Douglas McKee, director of vulnerability intelligence at Rapid7, stated: "AI agents give attackers a fresh set of connections to walk across... Each protocol was built assuming it lived on its own, so each one checks its own front door while nobody watches the hallway in between" [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗[14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. Mohiuddin describes "protocol pivoting" as "a multi-step attack in which an adversary gains initial access through one protocol, exploits trust assumptions between protocols, and escalates to capabilities only accessible via a different protocol" [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. Google’s fix involved applying an allow-list of IP ranges and block lists, rejecting unsafe base URLs at startup. Mohiuddin noted this is "more work than most MCP servers have done" [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. Google and Rapid7 have both fixed the flaws Mohiuddin reported [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗[14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗.
The Analysis. The Model Context Protocol (MCP) introduces systemic risks by defaulting to trust between agents, creating attack surfaces that bypass traditional security boundaries. The ability to repackaged malicious instructions as trusted internal messages allows attackers to evade content filters and execute commands within privileged contexts [15]aidailypost.comMCP Agent Protocol Flaw Exposes Chain-of-Trust RiskEditorial synthesis of the chain-of-trust risk, emphasizing the structural nature of the flaw across diverse organizations.Open source ↗. The SSRF vulnerability in Google’s MCP toolbox demonstrates how minor configuration errors (lack of redirect checks) can enable significant lateral movement across network segments [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. The concept of "protocol pivoting" describes a sophisticated attack methodology that leverages trust assumptions between disparate systems to escalate privileges [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. Although Google and Rapid7 have patched the specific flaws, the underlying trust between agents is a structural design issue that individual fixes do not resolve [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗[14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. The inclusion of financial institutions like JP Morgan Chase alongside tech giants underscores the cross-sector nature of this threat [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗.
Compass Outlook. The structural flaws in MCP represent a foundational risk to the integrity of AI agent networks. Without rigorous validation of trust chains and strict IP allow-listing, organizations remain vulnerable to lateral movement attacks that can compromise sensitive data or execute unauthorized actions [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗[15]aidailypost.comMCP Agent Protocol Flaw Exposes Chain-of-Trust RiskEditorial synthesis of the chain-of-trust risk, emphasizing the structural nature of the flaw across diverse organizations.Open source ↗. Because the weakness lies in the trust agents place in one another rather than in a single product, fixes to individual servers do not by themselves close the exposure [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗[15]aidailypost.comMCP Agent Protocol Flaw Exposes Chain-of-Trust RiskEditorial synthesis of the chain-of-trust risk, emphasizing the structural nature of the flaw across diverse organizations.Open source ↗.
Decision Window. Audit all MCP server configurations for proper IP validation and redirect policies, particularly those handling sensitive credentials. Monitor vendor patch releases for vulnerabilities similar to CVE-2026-97228 and Rapid7’s SSRF flaws [14]europesays.comMCP for agent-to-agent comms may be the riskiest protocol you've never heard ofRepublished analysis including the "protocol pivoting" definition and expert quotes from Rapid7’s McKee.Open source ↗. Assess the readiness of internal AI agent networks against protocol pivoting attacks by simulating trust chain exploitation scenarios.
Compass Strategic Intelligence
Compass Strategic Intelligence
Closing Outlook
These five signals leave readers watching next for the convergence or divergence of their respective trajectories. In Irkutsk, the critical question is whether the second reported death confirms a plague cluster or remains an isolated anomaly [2]mirror.co.ukInside Russia's 'plague cover-up' from second death to doctor's warning for BritsRospotrebnadzor reports that 60% of those under quarantine have been released. The U.S. State Department and White House are monitoring the situation, with the President noting willingness to assist regarding the "disproportionately…Open source ↗. In aviation security, the investigation into Hamam al-Hammami’s Australian links will determine if this was an individual radicalization event or part of a broader network [4]abc.net.auAFP confirms investigation of flydubai co-pilot's Australian linksThe AFP confirmed it is investigating the man's links to Australia but provided no further details at this stage. Authorities are examining whether al-Hammami was radicalized while in Australia, with sources indicating he may have visited…Open source ↗. Ukraine’s digital resilience depends on the speed of air defense replenishment and the effectiveness of infrastructure hardening against continued Geran-5 strikes [7]theguardian.comRussia strikes at heart of Ukraine’s digital economy with attacks on ISPs and datacentresReports of internet outages affecting approximately 100,000 households; Ukraine's struggle with air defense exhaustion regarding Patriot missiles; reports that Donald Trump approved licenses for domestic Patriot missile production.Open source ↗[9]kyivindependent.comRussia puts Ukraine’s internet in its sights as attacks on Kyiv infrastructure intensifyDetails of September 23–24 Geran-5 strikes on Solomianskyi data centers; specific provider damage reports for UTELS, Pavutyna, Crazy Network, and Etherlink; Russia's unverified claims regarding New-Telco and United DC; warnings from…Open source ↗. Denmark’s data breach highlights the enduring risk of third-party access to sovereign databases, with long-term implications for citizen trust and security posture [11]straitstimes.comDenmark government data leak exposes 8.8 million recordsConfirms 8.8M figure; details minister quotes; notes access status ambiguity; AI-generated content disclaimer.Open source ↗. Finally, the AI agent ecosystem must contend with a structural trust flaw in MCP that individual patches do not fully resolve [13]arstechnica.comVulnerability in agents from Google and others exposes structural flaw in MCPDetailed technical breakdown of the SSRF flaw in Google’s MCP toolbox and Rapid7’s CVE.Open source ↗[15]aidailypost.comMCP Agent Protocol Flaw Exposes Chain-of-Trust RiskEditorial synthesis of the chain-of-trust risk, emphasizing the structural nature of the flaw across diverse organizations.Open source ↗. The absence of confirmed crosscurrents among these signals suggests that each requires distinct strategic management, but collectively they underscore the fragility of modern systems when faced with coordinated or opportunistic threats.